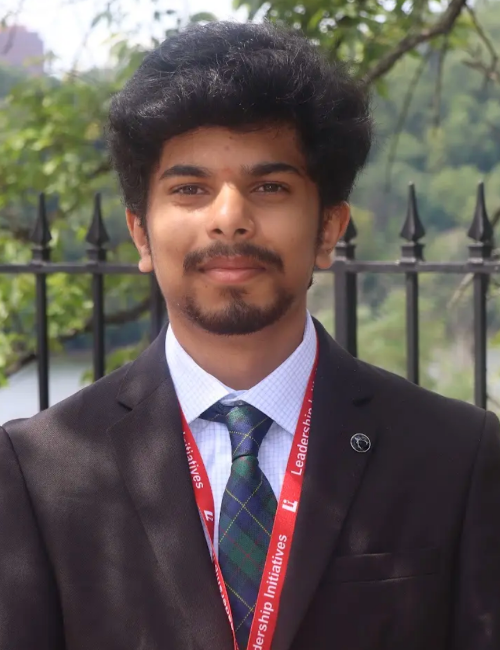
Vaishnav Kumar Parupally
My Cybersecurity Training
Knope
Quick Facts
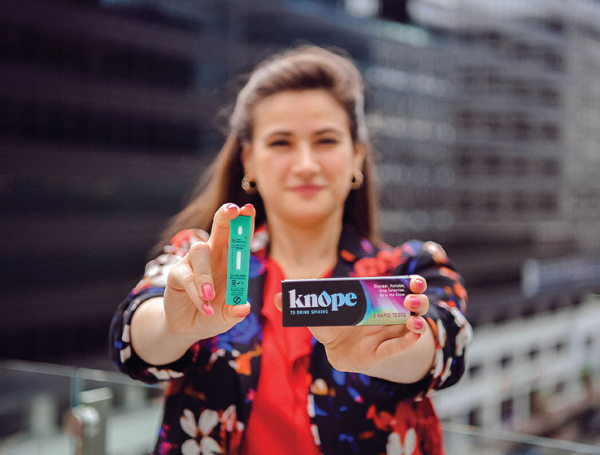
Knope is a small business founded by Danya Sherman in 2017 and based in Arlington, Virginia. It was created to help prevent drink spiking through safety solutions and increased public awareness.
Knope develops safety products designed to give individuals greater protection in social environments where drink spiking may occur.
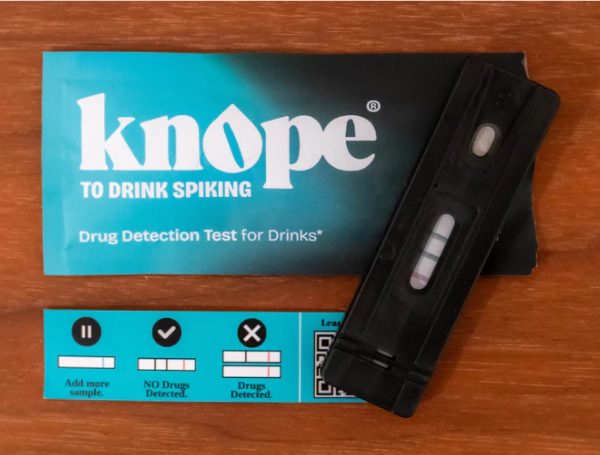
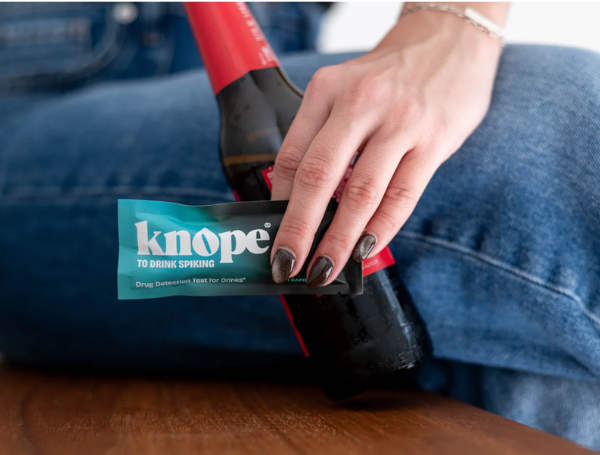
Its products include the Knope Test drink-spiking detector and reusable drink covers, which can be used at bars, restaurants, concerts, parties, and other social settings.
Knope works alongside Knomore, a nonprofit organization focused on education and advocacy, to combine practical prevention tools with broader public awareness efforts.
Knope
About the Organization
Knomore is the nonprofit organization associated with Knope and is dedicated to educating the public about the risks and dangers of drink spiking.
The organization focuses on education, public awareness, advocacy, and prevention, complementing Knope’s development of physical drink-safety products.
Knomore works to give individuals greater knowledge about drink spiking while encouraging preventative measures that can make social environments safer.
Together, Knope and Knomore combine safety products with education and advocacy to protect the public and increase awareness of drink-spiking risks.
Knope
Community Involvement
Knope developed the “What Now” Campaign, which partners Knomore with law enforcement to raise awareness about drink spiking and strengthen prevention efforts.
Knomore builds partnerships with schools, businesses, and community organizations to broaden the reach of its education and advocacy initiatives.
Knope also has opportunities to expand partnerships with colleges, universities, bars, restaurants, festivals, and event venues, particularly in settings where drink-spiking prevention is highly relevant.
These collaborations allow Knope and Knomore to connect prevention resources, community education, and public-safety expertise with individuals in social environments where drink spiking may occur.
Knope
Sources of Funding
The provided materials do not identify specific grants, foundations, government funding, or individual donors supporting Knomore, so these sources should not be assumed.
Knope operates as a small business and generates revenue through the development and sale of drink-safety products, including its drink-spiking detection tests and reusable drink covers.
Knomore functions as the nonprofit education and advocacy component of the broader drink-spiking prevention effort, working alongside Knope on public awareness and community partnerships.
Additional financial records or information directly from Knomore would be necessary to identify its specific charitable funding sources and how those funds are allocated.
My Security Presentation
During the Cybersecurity & Defense Internship, I worked with Beth Cerrone and Jamie Kreider to learn the basics of cybersecurity and explore its practical applications.
Throughout the week, I worked with a nonprofit to develop cybersecurity solutions to protect against various cyber threats. I worked with my team to analyze the threats to the organization and then developed a comprehensive solution.
At the conclusion of this internship, our team pitched the final proposal to the Leadership Initiatives Grant Committee, earning a microgrant to support the implementation of our proposal.

My Security Proposal Presentation
Throughout the program, we partnered with Knope's leadership team to evaluate the organization's internal cybersecurity posture and identify opportunities to strengthen the protection of company systems and sensitive business information.
Through these discussions, we determined that the most significant challenge facing Knope is the reliance on employee owned devices without centralized security management, increasing the organization's exposure to phishing, malware, and unauthorized access to confidential company data.
To address these vulnerabilities, we created a comprehensive cybersecurity proposal informed by recognized security frameworks and best practices. We recommended implementing a formal Bring Your Own Device policy supported by Cloudflare Zero Trust, Bitdefender endpoint protection, Action1 automated patch management, and Hexnode mobile device management to verify devices, secure endpoints, and improve visibility across the organization's environment. We also proposed establishing a formal incident response plan that provides employees with clear procedures for responding to cybersecurity events. Together, these recommendations will strengthen internal security controls, improve the organization's ability to detect and respond to threats, and better protect Knope's critical business operations and intellectual property.
Internship Highlights
I was given the unique opportunity to take exclusive tours of multiple government and security sites to speak directly with security professionals. During these tours, I was able to witness firsthand how cybersecurity operates at the national and international level.
I was able to visit the United States’ Security Innovation Lab. Throughout this visit, I was able to learn firsthand from government officials regarding how the government funds and establishes cyber-intelligence and cyber-counterintelligence technology.
We also toured the Homeland Security Investigations' (HSI) Technical Operations Center. During this visit, we learned how the government uses technology to track major crimes including wire-fraud, human trafficking, child exploitation, and more.
In order to apply the skills I learned throughout the internship, I worked directly with an organization based in the Washington, D.C. area, Knope, to discuss their company's cybersecurity needs.
After three meetings where I walked through the organization model, protected information, and staff training of the nonprofit, I worked with my team to create a staff training protocol and threat analysis for my partner.
At the end of the internship, I advocated on behalf of, and received funding for, my organization partner to implement the cybersecurity training protocols so they can best protect their client information and continue to develop with a reduced fear of cyberattacks and cybersecurity threats.
To learn more about the world of cybersecurity, I was given the unique opportunity to speak directly with cybersecurity experts from multiple organizations and backgrounds.
I worked directly with one of the leading consultants in Cyber Threat Management, and a lead Cyber Consultant from Ernst & Young, Phuong Nguyen, to learn about common threat assessment and cybersecurity counterintelligence. I also heard from the Director of Government Compliance for KPMG, Lisa Mathews, and a former Department of Justice Prosecutor, Brian Levine.
Throughout the internship, I also heard presentations from and spoke with representatives from the Department of Defense, Department of Homeland Security, and the National Security Agency. To learn the physical side of cybersecurity, we also had the unique opportunity to meet with globally recognized penetration testers and network threat assessors.
In order to put the skills we learned to the test, I had the unique opportunity to work with cybersecurity software typically used in graduate-level instructional courses. This provided me with a hands-on environment to develop and apply a wide range of cybersecurity skills.
I began with network cybersecurity, completing labs focused on network security and Linux to gain a deeper understanding of how networks communicate and where vulnerabilities may arise. This experience highlighted the ways in which cybersecurity threats can disrupt or compromise these communications, reinforcing the importance of proactive defense measures.
Building on these Linux skills, I participated in capture-the-flag coding competitions and explored virtual rooms designed to simulate real-world cybersecurity challenges. These activities tested both my technical abilities and problem-solving skills, allowing me to apply classroom concepts in practical, scenario-based settings.